$43.99
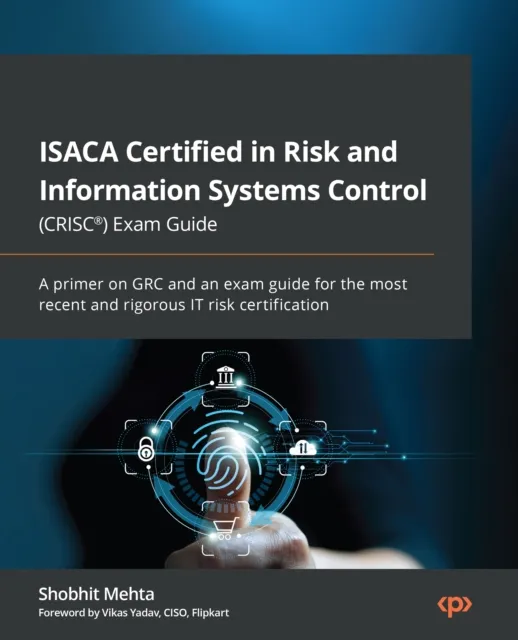
ISACA Certified in Risk and Information Systems Control (CRISC(R)) Exam Guide
A primer on GRC and an exam guide for the most recent and rigorous IT risk certification
Prepare to pass the ISACA CRISC exam with confidence, gain high-value skills, and propel yourself toward IT risk management mastery
Key Features
Gain end-to-end coverage of all the topics assessed in the ISACA CRISC exam
Apply and embed your learning with the help of practice quizzes and self-assessment questions
Have an in-depth guide handy as you progress in your enterprise IT risk management career
Purchase of the print or Kindle book includes a free PDF eBook
Book Description
For beginners and experienced IT risk professionals alike, acing the ISACA CRISC exam is no mean feat, and the application of this advanced skillset in your daily work poses a challenge. The ISACA Certified in Risk and Information Systems Control (CRISC®) Certification Guide is a comprehensive guide to CRISC certification and beyond that’ll help you to approach these daunting challenges with its step-by-step coverage of all aspects of the exam content and develop a highly sought-after skillset in the process.
This book is divided into six sections, with each section equipped with everything you need to get to grips with the domains covered in the exam. There’ll be no surprises on exam day – from GRC to ethical risk management, third-party security concerns to the ins and outs of control design, and IDS/IPS to the SDLC, no stone is left unturned in this book’s systematic design covering all the topics so that you can sit for the exam with confidence. What’s more, there are chapter-end self-assessment questions for you to test all that you’ve learned, as well as two book-end practice quizzes to really give you a leg up.
By the end of this CRISC exam study guide, you’ll not just have what it takes to breeze through the certification process, but will also be equipped with an invaluable resource to accompany you on your career path.
What you will learn
Adopt the ISACA mindset and learn to apply it when attempting the CRISC exam
Grasp the three lines of defense model and understand risk capacity
Explore the threat landscape and figure out vulnerability management
Familiarize yourself with the concepts of BIA, RPO, RTO, and more
Get to grips with the four stages of risk response
Manage third-party security risks and secure your systems with ease
Use a full arsenal of InfoSec tools to protect your organization
Test your knowledge with self-assessment questions and practice quizzes
Who this book is for
If you are a GRC or a risk management professional with experience in the management of IT audits or in the design, implementation, monitoring, and maintenance of IS controls, or are gearing up to take the CRISC exam, then this CRISC book is for you. Security analysts, penetration testers, SOC analysts, PMs, and other security or management professionals and executives will also benefit from this book. The book assumes prior experience of security concepts.